Proactive, flexible IT services designed to keep your business secure, connected and productive — while reducing costs and complexity.
NIS2 Compliance Readiness for Businesses in Ireland
Landmark Technologies helps businesses in Ireland assess their IT environment, identify potential cybersecurity gaps and strengthen the technical controls that support NIS2 compliance and preparation.
What Is NIS2?
NIS2 is an EU cybersecurity directive designed to raise and harmonise the level of cybersecurity across the European Union.
It replaces the original NIS Directive and significantly expands its scope, bringing more sectors and organisations into the cybersecurity framework.
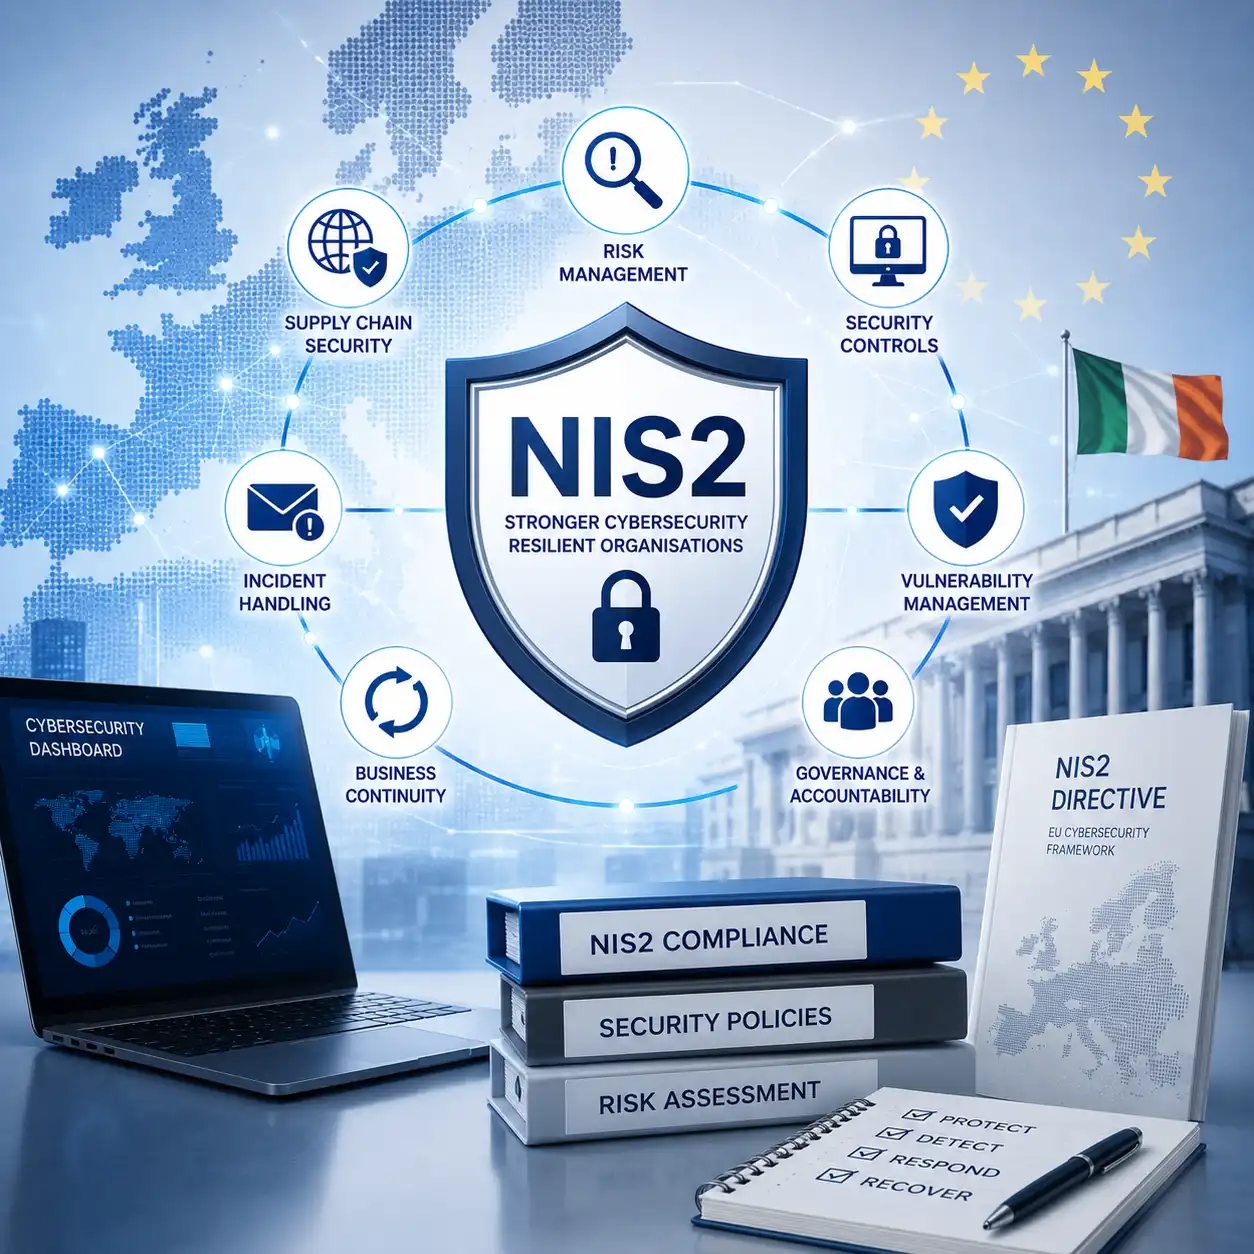
NIS2 introduces stronger requirements around cybersecurity risk management, incident handling, business continuity, supply chain security, vulnerability management and security controls.
For businesses in Ireland, the practical message is simple:
Cybersecurity needs to be treated as an ongoing business risk, not just an IT issue.
NIS2 Compliance Requirements
NIS2 takes a risk-management approach to cybersecurity. Rather than focusing on one particular technology, organisations need appropriate technical, operational and organisational measures to manage cybersecurity risk.
Risk Analysis & Cybersecurity Policies
Identify cybersecurity risks, understand your critical systems and establish appropriate security policies and controls.
Incident Management
Have processes in place to detect, respond to and manage cybersecurity incidents.
Business Continuity & Disaster Recovery
Prepare for disruption with appropriate backup, recovery and business continuity measures.
Supply Chain Security
Consider cybersecurity risks associated with suppliers, service providers and other third parties.
Vulnerability Management
Identify vulnerabilities and manage software updates, patches and remediation.
Network & Systems Security
Protect networks, systems and devices through appropriate technical security controls and secure configuration.
Access Control & Authentication
Control who can access systems and information using appropriate authentication and access management measures, including multi-factor authentication where appropriate.
Cryptography & Encryption
Use appropriate cryptographic and encryption measures where relevant to the organisation’s risks and systems.
Cybersecurity Training
Support cybersecurity awareness and good cyber hygiene across the organisation.
Incident Reporting
Organisations within scope may have obligations to report significant cybersecurity incidents to the relevant national authorities within defined timeframes.
How to Prepare for NIS2 Compliance
A practical NIS2 compliance preparation process can start with your existing IT environment, current security controls and the risks most relevant to your organisation.
1. Determine Whether You May Be in Scope
Review your sector, organisation size, activities and type of entity.
2. Understand Your Cybersecurity Posture
Identify the systems, devices, users, data and services that are important to your business.
3. Identify Potential Security Gaps
Review existing cybersecurity controls and identify areas that may require improvement.
4. Review Access Controls
Check user permissions, privileged access, authentication and MFA.
5. Review Network & Device Security
Look at endpoint protection, network security, secure configuration and device management. Explore our Cybersecurity Services for wider protection across your IT environment.
6. Review Vulnerability & Patch Management
Make sure vulnerabilities and software updates are identified and addressed consistently. Regular Vulnerability Scanning can help identify weaknesses before they become serious security risks.
7. Review Backup & Recovery
Check whether critical business data and systems can be recovered following an incident. Landmark’s Online Backup solutions can support stronger recovery and business continuity.
8. Consider Incident Response
Make sure there is a practical process for identifying, escalating and responding to cybersecurity incidents.
9. Review Third-Party Risk
Consider the cybersecurity risks associated with IT suppliers, cloud services and other critical providers.
10. Build a Remediation Plan
Prioritise the gaps that present the greatest risk and create a realistic plan for improving your security controls.
How Landmark Supports NIS2 Compliance
Practical IT Support for Your NIS2 Preparation
NIS2 can look complicated when viewed purely as a regulatory requirement.
From an IT perspective, many of the questions come down to something more practical:
Are your systems, devices, users, networks, backups and security controls properly protected?
For wider support with regulatory preparedness, risk and technical governance, explore our Compliance & Governance services.
Assess Your Environment
Review your current IT systems, devices, users and security controls.
Identify Security Gaps
Identify areas of your cybersecurity environment that may require attention or improvement.
Strengthen Technical Controls
Improve the technical foundations that support stronger cybersecurity and NIS2 compliance.
Landmark Technologies can support businesses in Ireland with the technical and IT aspects of NIS2 compliance and preparation.
Prepare Your IT Environment for NIS2 Compliance
If your organisation may be affected by NIS2, understanding the security and resilience of your existing IT environment is an important place to start.
Talk to Landmark Technologies about assessing your current environment, identifying potential cybersecurity gaps and strengthening the technical controls that support NIS2 compliance.